 Linkedin

 Facebook
 Email
 more
Cybersecurity leadership when and where you need it
Cybersecurity increasingly affects business continuity, reputation, regulatory compliance and stakeholder confidence. Yet many organisations do not require a permanent CISO or lack the senior capacity needed to govern cyber risk effectively.
At the same time, increasing regulatory, insurance, client and audit expectations require clearer ownership, stronger governance and greater management visibility over cyber exposure.
CISO as a Service provides flexible, senior-led cybersecurity leadership aligned with your organisation’s business risks and priorities. It helps management clarify accountability, establish priorities, strengthen resilience and govern cybersecurity investment with greater confidence.
When does CISO as a Service fit?
CISO as a Service can provide additional leadership and structure when:
- cybersecurity ownership is unclear;
- regulatory, insurance or client expectations are increasing;
- management needs better visibility over cyber exposure;
- the organisation is preparing for ISO 27001 or another security framework;
- senior cybersecurity leadership is required without creating a permanent role.
What does CISO as a Service cover?
Our CISO as a Service model provides leadership across cybersecurity governance, risk, resilience and security priorities, connecting technical exposure with management accountability and business decisions.
Cybersecurity governance and risk management
Establish a structured approach to cybersecurity governance, risk oversight and management responsibilities.
Cyber strategy and roadmap
Define cybersecurity priorities and a roadmap aligned with business exposure, objectives and risk appetite.
Risk ownership and accountability
Clarify cyber risk ownership, responsibilities, decision rights and management oversight.
Third-party and supplier risk
Strengthen oversight of cybersecurity risks arising from critical suppliers and technology dependencies.
Incident governance and resilience
Strengthen governance around incident preparedness, response, continuity and recovery.
Data, privacy and AI security
Address cybersecurity considerations related to data, privacy and increasingly AI-enabled environments.
Board and Executive Committee reporting
Provide leadership with structured visibility over cyber exposure, priorities, decisions and progress.
Cybersecurity as a business risk
Cybersecurity should not be managed as a standalone technical discipline. A significant cyber incident can affect operations, customers, suppliers, regulatory obligations and the organisation’s ability to deliver critical services.
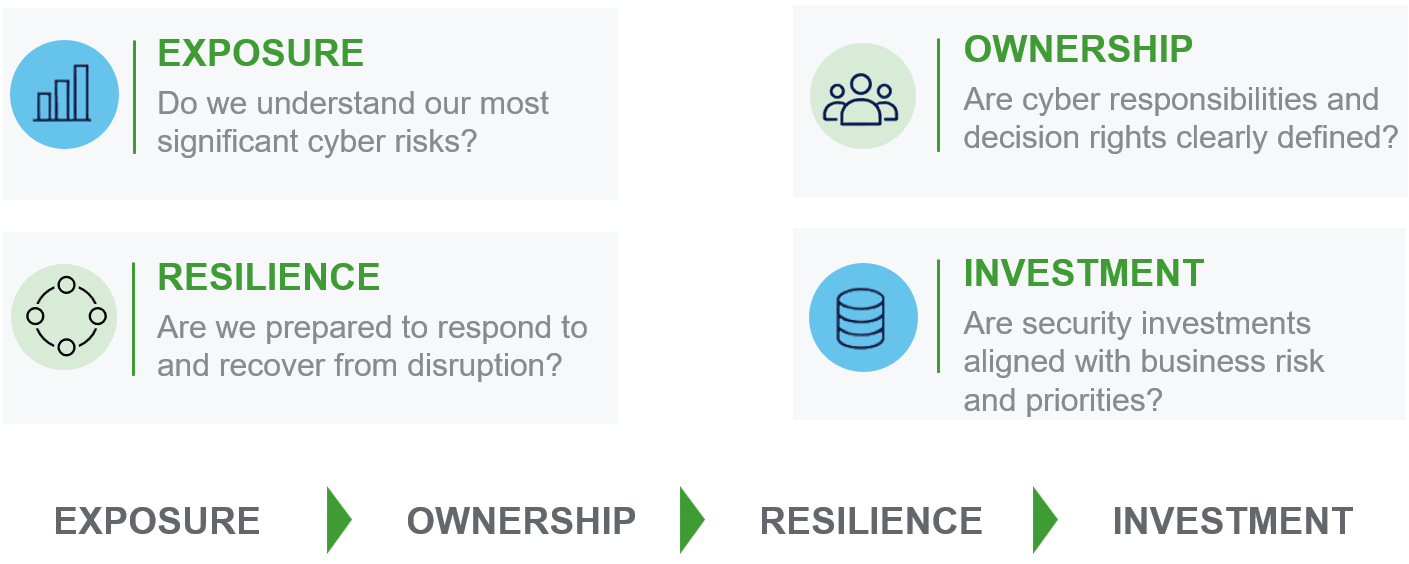
CISO as a Service connects cyber exposure with governance, ownership, resilience and investment decisions, helping management determine where attention and resources are required.
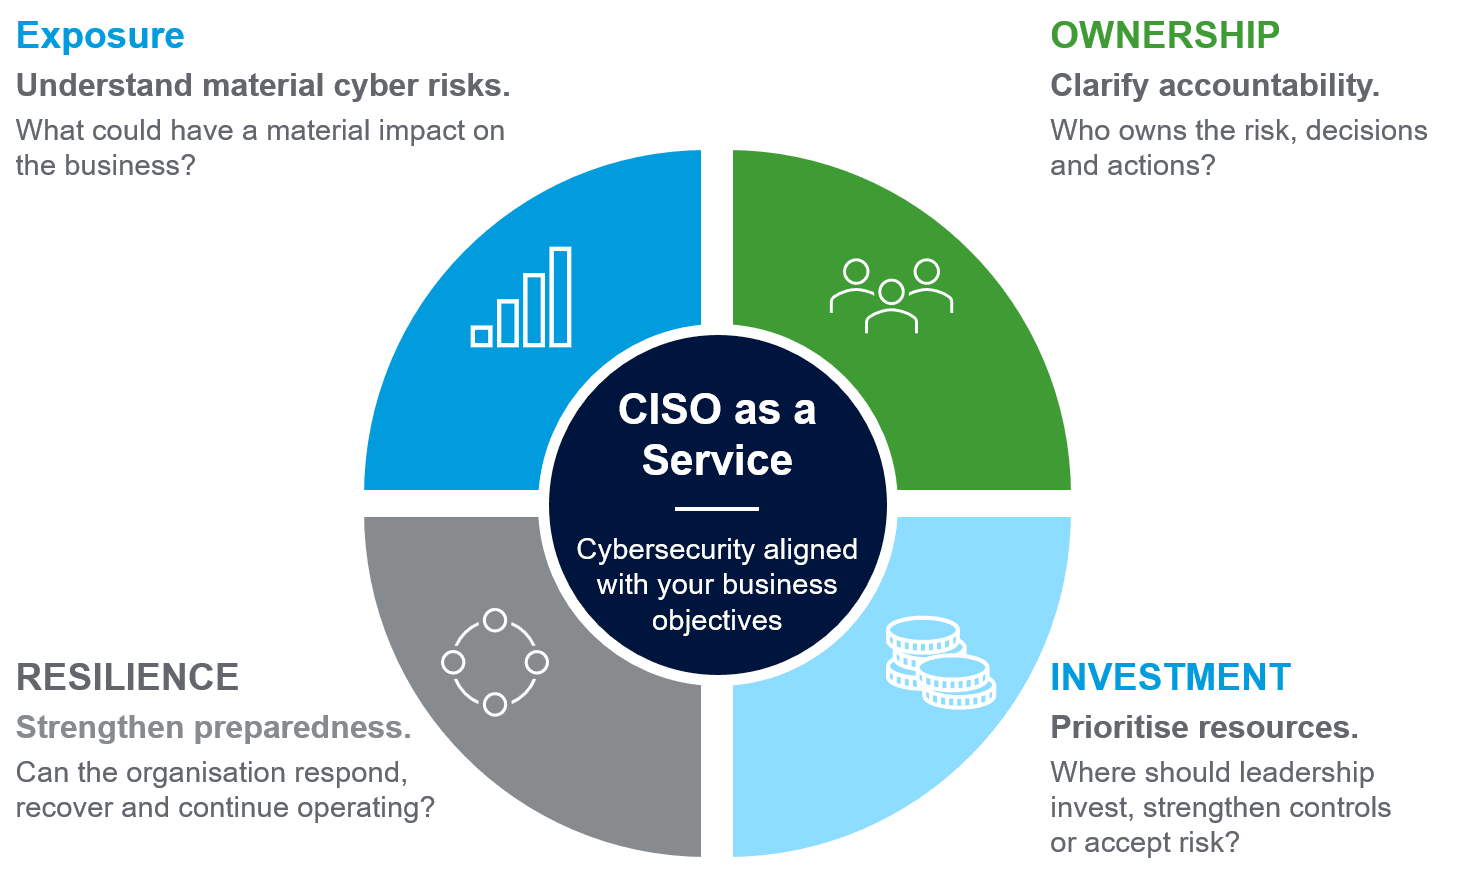
Effective cybersecurity governance connects risk exposure with clear ownership, resilient operations and informed investment decisions.
What do you receive?
The objective is not simply to strengthen cybersecurity controls. CISO as a Service provides management with clearer visibility, governance and priorities for managing cyber risk as a business issue.
Business-oriented view of cyber risks
A consolidated view of the cyber risks requiring management and leadership attention.
Defined governance and ownership
Clear cyber risk responsibilities, decision rights and accountability.
Prioritised security roadmap
A structured roadmap focused on the most important risks, dependencies and improvement priorities.
Board-level dashboard
Clear reporting to support management and Board-level oversight of cybersecurity.
Budget and investment priorities
Greater clarity over cybersecurity investment needs and priorities.
Continuous improvement programme
A structured approach to strengthening cybersecurity governance and maturity over time.
A flexible cybersecurity leadership model
CISO as a Service complements existing management, technology and security teams with experienced cybersecurity leadership at an agreed level of engagement.
The model is designed for organisations requiring senior cyber leadership and governance without necessarily creating a permanent internal CISO role.
Senior-led
Experienced cybersecurity leadership focused on management priorities and business risk.
Flexible
Leadership capacity adapted to your organisation’s exposure, maturity and requirements.
Accountable
Clear governance, responsibilities, decision rights and management reporting.
From discussion to action
Our approach moves from cyber exposure and business context to clearer priorities, ownership and coordinated action.
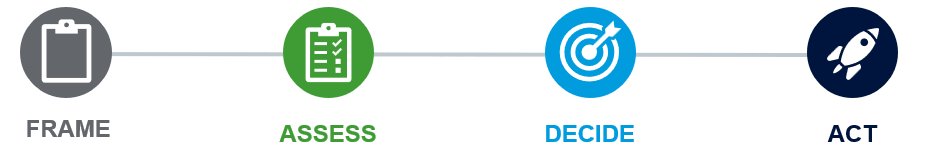
Frame
Clarify the business context, cybersecurity concerns, decisions and constraints.
Assess
Establish cyber exposure, priorities, dependencies and leadership needs.
Decide
Agree priorities, governance, ownership and risk responses.
Act
Mobilise the cybersecurity roadmap and agreed next steps.
Related cybersecurity capabilities
Cybersecurity & Digital Resilience
Specialist capabilities supporting cyber risk assessment, resilience, security improvement and implementation needs.
Discover Cybersecurity & Digital Resilience
Regulatory & Compliance Governance
Support in translating cybersecurity and technology-related regulatory obligations into governance, controls and management action.
Discover Regulatory & Compliance Governance
Explore CISO as a Service in more detail
Discover how CISO as a Service provides flexible cybersecurity leadership across governance, risk, resilience and investment priorities.