 Linkedin

 Facebook
 Email
 more
Cybersecurity is no longer only about preventing attacks. Organisations need to understand their exposure, strengthen their ability to withstand disruption and ensure that people, processes and technology work together to protect critical operations.
RSM Switzerland helps organisations assess cyber exposure, strengthen controls and resilience, improve preparedness and build a stronger cybersecurity culture.
Cybersecurity requires more than technical protection
Cyber threats continue to evolve across systems, data, suppliers, payment processes and human interactions. An incident can lead to financial loss, operational disruption, regulatory exposure and reputational damage.
Effective cybersecurity therefore requires a coordinated approach combining risk assessment, practical controls, resilience, incident preparedness and people awareness.
We help organisations understand where they are most exposed and strengthen the measures required to prevent, withstand and recover from cyber disruption.
Where should organisations strengthen their cyber resilience?
EXPOSURE
Where are our most significant cyber vulnerabilities and dependencies?
PROTECTION
Are our controls proportionate to our exposure and business needs?
RESILIENCE
Can critical operations continue and recover when disruption occurs?
AWARENESS
Are our people prepared to recognise and respond to cyber threats?
What does Cybersecurity & Digital Resilience cover?
Cyber risk and maturity assessments
Assess cybersecurity exposure, vulnerabilities, controls and maturity to identify the areas requiring attention and prioritised improvement.
Security controls and risk mitigation
Review and strengthen security measures across technology, processes, access rights and other areas of cyber exposure.
Digital resilience and preparedness
Strengthen the organisation’s ability to maintain critical operations, respond to disruption and recover effectively.
Incident preparedness and response
Clarify incident processes, responsibilities, escalation mechanisms and preparedness before disruption occurs.
Third-party cyber risk
Assess and strengthen oversight of cybersecurity dependencies arising from suppliers, service providers and other critical third parties.
Data and privacy security
Support appropriate cybersecurity measures around sensitive data, access, information handling and privacy-related exposure.
Cybersecurity awareness and human risk
Strengthen employee awareness and preparedness through training, simulations and practical awareness measures.
Build resilience before disruption occurs
Digital resilience is the ability to maintain critical activities when technology, data, suppliers or cyber incidents disrupt normal operations.
Resilience therefore goes beyond prevention. Organisations need to understand critical dependencies, prepare appropriate responses and ensure that recovery measures are realistic and coordinated.
Our approach helps organisations strengthen:
- critical technology and operational dependencies;
- incident preparedness;
- continuity and recovery arrangements;
- governance and escalation;
- supplier resilience;
- testing and preparedness exercises.
Cyber resilience is not simply about preventing disruption. It is about being prepared to respond, recover and continue operating.
People are a critical part of cyber resilience
Technology alone cannot address cybersecurity risk. Human behaviour, weak processes and insufficient awareness can create significant exposure even when technical controls are in place.
We help organisations strengthen their human layer of defence through structured and measurable cybersecurity awareness activities.
Cybersecurity awareness training
Interactive training designed to strengthen understanding of cyber threats and secure behaviours.
Phishing simulations
Practical simulations adapted to the organisation’s context to identify exposure and reinforce employee preparedness.
Breach and exposure monitoring
Monitoring capabilities to identify potential compromised information and areas requiring attention.
Policy management and tracking
Structured support to communicate, maintain and track relevant cybersecurity policies and awareness requirements.
Expert-led workshops
Practical sessions covering topics such as cyber hygiene, social engineering, password security and incident response.
From awareness to measurable improvement
Cybersecurity awareness should not be a one-off training exercise.
Effective awareness programmes should allow organisations to understand human exposure, monitor engagement, identify recurring weaknesses and demonstrate improvement over time.
Our approach combines training, simulations, monitoring and expert support to help organisations build stronger and more sustainable security behaviours.
Cybersecurity and fraud-related controls
Cyber threats and fraud schemes frequently exploit human behaviour, access rights and weaknesses in business processes.
We can support organisations in reviewing cyber-related controls around areas such as:
- payment and banking-detail changes;
- access rights and segregation of duties;
- verification and escalation procedures;
- social engineering exposure;
- sensitive data handling.
From assessment to stronger resilience
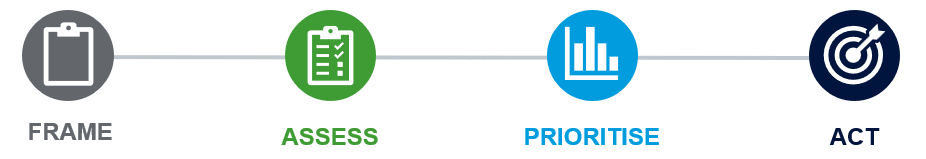
FRAME
Clarify the business context, critical operations, cyber concerns and constraints.
ASSESS
Establish exposure, vulnerabilities, dependencies and preparedness.
PRIORITISE
Identify the controls, resilience measures and awareness priorities requiring attention.
STRENGTHEN
Implement agreed improvements and support continuous resilience.
Connected to CISO as a Service
Cybersecurity & Digital Resilience provides specialist assessment, resilience and security capabilities that can be mobilised through CISO as a Service.
Where organisations need ongoing senior cybersecurity leadership, clearer ownership, Board-level visibility and governance of security investment, CISO as a Service provides the executive leadership structure required to coordinate the wider cyber agenda.


