 Linkedin

 Facebook
 Email
 more

Technology is increasingly embedded in critical business processes, financial reporting and decision-making. As organisations rely on complex systems, cloud services, ERP platforms, applications and third-party providers, confidence in the underlying technology and controls becomes increasingly important.
RSM Switzerland provides independent Technology Assurance to help management, Boards, audit teams and other stakeholders understand whether technology environments and controls are appropriately designed, governed and operating as expected.
Confidence in increasingly complex technology environments
Technology assurance goes beyond reviewing individual IT controls. It considers how systems, applications, processes and dependencies support critical business activities and how effectively associated risks are managed.
Our approach provides an independent perspective on areas such as control effectiveness, data integrity, system availability, access management, resilience and technology governance.
The objective is to identify control weaknesses, understand their potential impact and provide clear insights that support management and assurance activities.
When is Technology Assurance relevant?
Technology Assurance can provide additional confidence when:
- critical business processes depend heavily on technology;
- management or auditors require assurance over IT controls;
- ERP or other significant systems are implemented or changed;
- cloud environments or outsourced technology services introduce new dependencies;
- control weaknesses or technology risks require independent assessment;
- financial, internal or regulatory assurance activities depend on reliable systems and data.
CONTROLS
Are key technology controls appropriately designed and operating effectively?
SYSTEMS
Can we rely on the systems and applications supporting critical processes?
EVIDENCE
Can management and stakeholders demonstrate that key controls operate as expected?
CONFIDENCE
Do assurance activities provide sufficient visibility over technology risk?
What does Technology Assurance cover?
IT general controls
Assess governance and controls across areas such as access management, change management and technology operations.
Application controls
Assess automated and system-based controls supporting critical processes, transactions and information.
Systems and business processes
Review how technology supports critical business processes and whether relevant controls, interfaces and dependencies operate effectively.
ERP assurance
Provide independent assurance around ERP controls, implementations, migrations and technology-enabled business processes.
Cloud and digital environments
Assess governance, controls and dependencies associated with cloud platforms and increasingly connected digital environments.
Data integrity and reliability
Assess technology-related controls supporting the completeness, accuracy and reliability of critical information.
Third-party technology assurance
Assess controls and technology dependencies involving outsourced service providers and other critical third parties.
Technology Assurance across the technology lifecycle
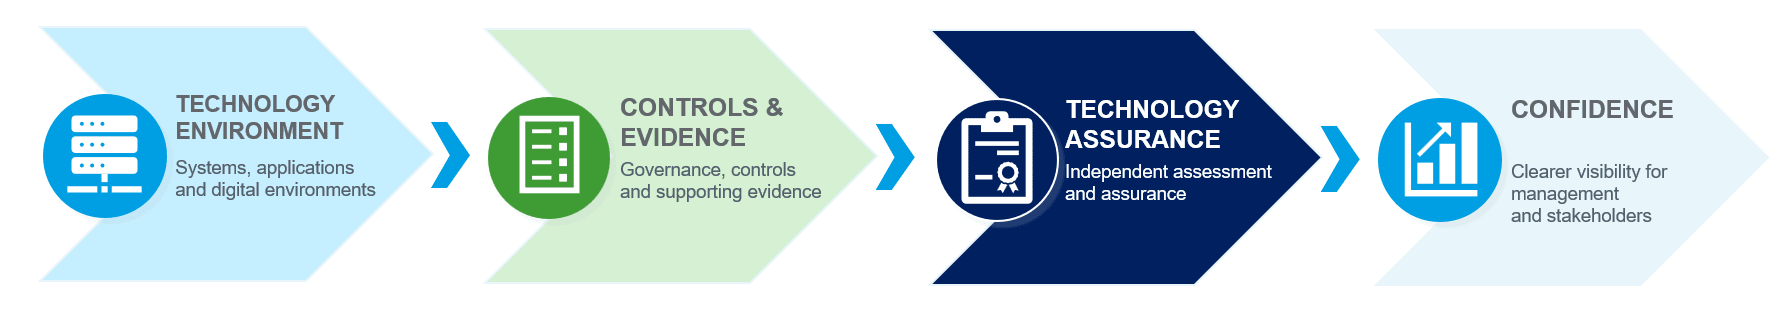
Technology Assurance connects technology environments, controls and evidence to provide management and stakeholders with greater confidence.
Supporting financial and internal audit
Technology controls can have a direct impact on financial reporting, internal controls and the reliability of information used by management and auditors.
Technology Assurance can support financial and internal audit activities by providing specialist assessment of technology environments, IT general controls, application controls and system-supported processes.
Our teams work with audit, risk and management stakeholders to ensure that the technology dimension is assessed in the appropriate business and assurance context.
Assurance over technology change
Significant technology change can alter control environments, introduce new dependencies and affect the reliability of critical systems and information.
Technology Assurance provides an independent perspective during or following initiatives such as:
- ERP implementations and migrations;
- cloud adoption;
- significant system changes;
- digital transformation programmes;
- outsourcing and third-party technology arrangements;
- implementation of new automated controls.
The objective is not to manage the transformation programme, but to provide independent assurance over relevant technology risks and controls.
A risk-based and tailored assurance approach
Every organisation has a different technology environment, risk profile and assurance requirement.
Our approach focuses on the areas that matter most, considering:
Business criticality
Which systems, processes and information are essential to business operations?
Technology exposure
Where are the most significant technology and control risks?
Assurance objectives
What does management, Audit or another stakeholder need confidence over?
Evidence
What information and testing are required to support an assurance conclusion?
What do you receive?
Independent assessment
A structured and objective view of the technology environment and controls in scope.
Clear findings
Identification of control weaknesses, technology risks and areas requiring attention.
Risk-based prioritisation
Findings considered according to business impact, criticality and assurance objectives.
Practical recommendations
Clear and proportionate recommendations designed to strengthen the control environment.
Assurance evidence
Structured documentation and evidence supporting management, audit or other assurance requirements.
Greater confidence
Improved visibility over the reliability, governance and control of critical technology environments.
From scope to assurance
01 | SCOPE
Define the technology environment, assurance objectives and key risks.
02 | ASSESS
Review relevant controls, systems, processes and supporting evidence.
03 | TEST
Evaluate control design and, where relevant, operating effectiveness.
04 | REPORT
Communicate findings, risk implications and recommendations.
Complementary to Technology Risk & Advisory
Technology Assurance complements our advisory services by providing an independent assurance perspective where management, Audit or other stakeholders require additional confidence over technology and controls.
Depending on the context, Technology Assurance can complement:
- IT Risk & Governance 360, where identified technology risks require deeper assurance;
- CIO as a Service, where significant investments or programmes require independent assurance;
- CISO as a Service, where cybersecurity governance or controls require assurance;
- Technology Transformation, where significant ERP, cloud or system changes require independent review.


